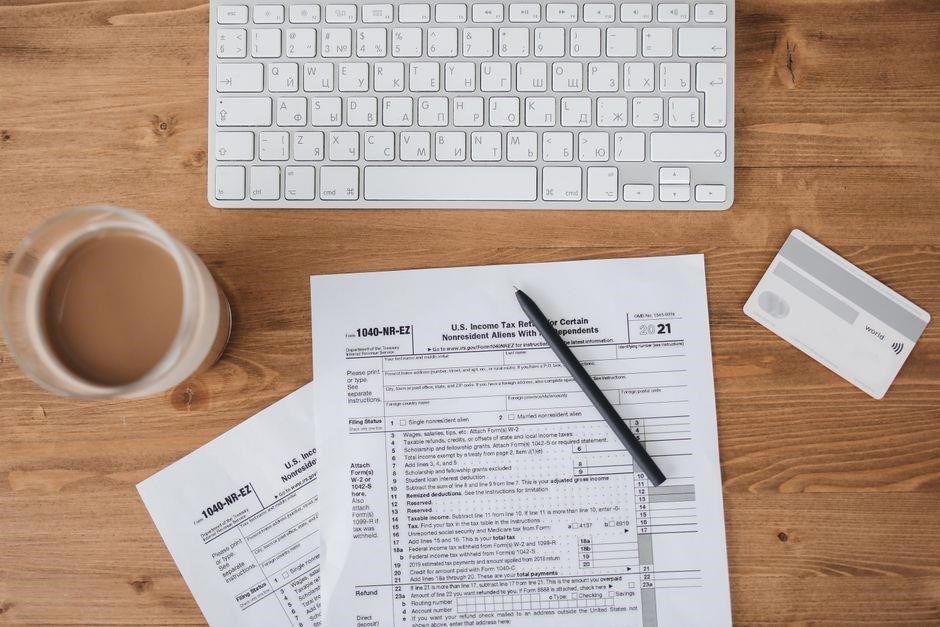
Overview of New Customer Credit Application Forms
New customer credit application PDFs streamline onboarding by capturing essential data—company details, trade references, banking info, and credit limits—in a single, legally compliant form. They enable automated risk assessment, protect against disputes, and support audit-ready documentation. Uniform flow!
Purpose and Benefits
The new customer credit application PDF serves as a single, standardized instrument that captures all necessary data for a credit decision. By consolidating company details, trade references, banking information, and requested credit limits into one form, businesses reduce manual data entry errors and accelerate the approval cycle.
Key benefits include:
- Risk Mitigation: The form’s structured fields enable automated scoring of payment history, financial ratios, and reference checks, providing a clear basis for extending credit.
- Legal Safeguard: A signed authorization clause within the PDF permits the creditor to verify information with third‑party agencies, protecting against disputes and compliance with data‑protection laws.
- Audit Readiness: Every completed form is archived in a searchable PDF repository, allowing auditors to trace decisions back to documented evidence and reducing the risk of regulatory penalties.
- Operational Efficiency: Signatures and auto‑populate features cut processing time by up to 40 %, freeing finance teams to focus on activities.
- Customer Experience: A user‑friendly PDF interface, accessible on desktop and mobile, encourages timely submission and reduces back‑and‑forth communication.
Overall, the PDF format delivers a transparent, repeatable, and compliant framework that aligns credit policy with business growth objectives.
Risk Assessment Components
Risk assessment in a new customer credit PDF hinges on credit score, payment history, trade references, and financial ratios. Structured fields allow automated scoring, flagging high risk accounts, supporting evidence‑based limits Use this form to enforce limitsdaily
Credit History Verification
Credit history verification is the cornerstone of a trustworthy new customer credit application PDF. By embedding a dedicated section that requests a company’s credit reference list, banking details, and a signed authorization to access third‑party credit reports, the form ensures that every potential client is subject to the same rigorous scrutiny. The process typically follows these steps:
- Reference Collection: The applicant supplies at least three trade references, including contact names, phone numbers, and email addresses. These references are then contacted to confirm payment terms, settlement speed, and any outstanding disputes.
- Banking Verification: Applicants provide bank account numbers and routing information. A quick API call to a banking verification service confirms the account’s validity and checks for recent overdrafts or account closures.
- Credit Report Request: With the signed authorization, the creditor can pull a credit report from a recognized credit bureau. The report includes payment history, delinquencies, and credit score.
- Data Consolidation: All collected data is automatically compiled into a single PDF, which can be stored in a CRM or shared with the risk team for scoring.
- Decision Logging: The final credit decision—approved, pending, or declined—is recorded in the PDF’s metadata, ensuring audit trails are complete.
Because the form is standardized, the risk team can quickly compare new applications against historical data, reducing the likelihood of gut‑instinct approvals. The result is a transparent, repeatable process that protects the business from bad debt while maintaining a smooth onboarding experience for legitimate customers.
In addition, the PDF can embed a digital signature field for the applicant’s authorized representative. This signature confirms that the information provided is accurate and that the applicant consents to the verification process. Digital signatures also satisfy regulatory requirements for data integrity and non‑repudiation, further strengthening the legal foundation of the credit decision.
Finally, the form’s structure allows for automated scoring algorithms to assign risk scores based on credit history, reference feedback, and banking health indicators. These scores can be visualized in a dashboard, giving the credit team instant insight into the applicant’s likelihood to pay on time. By integrating these components into a single PDF, companies can streamline compliance, reduce manual errors, and ensure every new customer undergoes the same level of scrutiny.
Thus, a well‑structured credit history verification section turns a simple form into a powerful risk‑management tool.
- Applicant name and registration number
- Trade reference contacts
- Bank account details
- Credit score range
- Authorized signature
This snapshot enables instant review by the risk team and decisions.
Legal Protection Features
Signature fields authorize data checks, ensuring compliance. A clause confirms consent to credit bureau access, protecting against disputes. The PDF logs decisions, providing audit trails that meet regulatory standards and safeguard the company’s legal interests. END!!!.
Authorization for Information Verification
Customers must sign a clear consent statement within the PDF, granting the creditor permission to access credit reports, banking records, and trade references. This clause is embedded in the form’s signature block, ensuring that the customer’s agreement is captured electronically or on paper. By including a specific authorization line—“I authorize the creditor to obtain and review my credit history, banking information, and trade references for the purpose of evaluating my creditworthiness”—the form meets regulatory requirements for data privacy and consent. The signature field is linked to a digital signature pad or a scanned image, allowing the creditor to verify authenticity before proceeding. This step protects the creditor from liability related to unauthorized data requests and provides a documented trail that can be referenced during audits or disputes. Additionally, the form includes a checkbox for the customer to acknowledge that they have read and understood the privacy policy, further reinforcing compliance with data protection laws such as GDPR or CCPA. The authorization section is designed to be concise yet comprehensive, ensuring that both parties are clear on the scope of information that may be accessed and the purpose of the verification. By embedding this clause directly into the PDF, the creditor can automate the verification process, trigger credit bureau queries, and store the signed consent securely in the customer’s file. The signed PDF is retained in a secure, cloud‑based archive, allowing rapid access for future credit reviews and ensuring compliance with evolving regulatory standards.
Compliance Requirements
New customer credit application PDFs must include signed consent for data access, audit trails, and retention policies. They should align with GDPR, CCPA, and local credit laws, ensuring data minimization, storage, and dispute resolution clauses. Compliance is mandatory fair.
Audit Documentation for Credit Decisions
Audit documentation is the backbone of defensible credit decisions. A new customer credit application PDF must capture every data point that feeds into the approval score: trade references, banking details, credit limits, and signed authorizations. Each entry should be timestamped and digitally signed to provide an immutable trail. The PDF should embed a checksum or hash that can be verified against the stored database record, ensuring that the document has not been altered post‑submission. Audit logs must record who reviewed the application, the date of review, and the final decision. These logs should be accessible via an audit portal or exported as CSV for regulatory review. Compliance frameworks such as ISO 27001 and SOC 2 require that all credit decision data be stored for a minimum of five years, with secure deletion thereafter. Additionally, the PDF must include a version control field so that any updates to the form are traceable. The audit trail should also capture any risk assessment scores assigned by automated systems, along with the rationale for manual overrides. Finally, a signed acknowledgment from the customer confirming receipt of the decision and understanding of the terms closes the loop, providing evidence that the customer was informed and consented to the credit terms. This comprehensive documentation protects the business against disputes, regulatory inquiries, and internal reviews, ensuring that every credit decision is transparent, repeatable, and defensible;
In practice, many firms integrate the PDF with an API that automatically populates fields from a credit bureau feed. The resulting audit file includes the bureau score, the date of the score, and the source identifier. When a customer is declined, the PDF should contain a clear explanation of the decision criteria, referencing the specific risk thresholds that were exceeded. This level of detail is essential during external audits, as regulators often request evidence of consistent application of credit policies. The audit documentation should also include any correspondence with the customer, such as emails or letters, that discuss the credit terms or address disputes. By maintaining a single, unified record in the PDF and its associated metadata, the organization can quickly demonstrate compliance during internal or external reviews, reducing the risk of penalties and preserving customer trust.
Standardization of Credit Applications
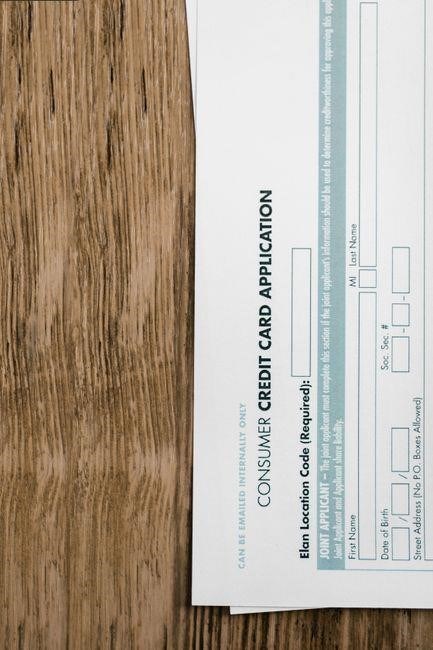
Uniform PDF forms enforce consistent data capture, reduce errors, and enable automated scoring. By standardizing fields—company, contact, banking, limits—organizations ensure repeatable, auditable decisions and streamline onboarding. Reduced manual effort ail
Avoiding Gut Instinct Approvals
Relying on instinct for credit decisions introduces bias, inconsistent risk assessment, and potential compliance gaps. A standardized PDF application forces each applicant to supply the same data set—company identifiers, contact details, banking information, trade references, and requested credit limits—ensuring that every review is based on comparable evidence. When the form mandates completion of all sections, incomplete submissions are automatically flagged and returned, preventing partial or rushed approvals. The embedded legal clause authorizing information verification protects the issuer by granting explicit permission to consult credit bureaus or reference checks, thereby grounding the decision in verifiable facts rather than anecdotal impressions. Moreover, the PDF’s structured fields feed directly into automated scoring engines or audit trails, creating a transparent, auditable record that satisfies regulatory scrutiny. By eliminating the discretionary “feel‑good” factor, companies reduce the risk of over‑extension, maintain consistent credit exposure limits, and reinforce a culture of data‑driven risk management. The result is a disciplined, repeatable approval workflow that aligns with best practices in credit governance and supports sustainable growth. Organizations that adopt this disciplined approach often observe a 20–30% reduction in overdue accounts and a measurable improvement in cash flow forecasting. The PDF format also facilitates seamless integration with ERP systems, allowing real‑time updates of credit limits and automated reminders for payment terms. Training staff to interpret the standardized fields further diminishes subjectivity, ensuring that every credit officer evaluates applicants against the same criteria. Ultimately, the shift from gut to data not only safeguards financial health but also strengthens customer relationships by demonstrating fairness and transparency. By embedding this structured approach, companies can also leverage analytics to identify trends, adjust credit policies proactively, and maintain a competitive edge in the marketplace. This consistency also eases audits, documenting each decision step and reinforcing compliance. It builds trust with stakeholders and supports long‑term financial stability!!!…
Standardized Approval Process Procedures
Implementing a uniform approval workflow for new customer credit applications ensures consistency, reduces risk, and aligns with regulatory expectations. The process begins when a completed PDF form is submitted electronically; mandatory fields—such as company registration number, VAT identifier, trade references, and requested credit limit—are automatically validated for completeness. Once the form passes validation, it is routed to the credit committee via an integrated workflow engine. Each committee member receives a notification, and the system logs the timestamp, reviewer identity, and any comments. Decision logic is embedded in the workflow: if the applicant’s credit score exceeds the predefined threshold, the application is auto‑approved; if it falls below, the case escalates to a senior analyst for manual review. All decisions are recorded in a central database, providing an audit trail that can be queried for compliance audits or dispute resolution. The workflow also triggers automated communication: approved customers receive a digital credit agreement signed via e‑signature, while declined applicants receive a courteous notification with an explanation. Additionally, the system updates the customer’s credit file in the ERP, adjusting the credit limit and payment terms accordingly. By standardizing each step—from data capture to final approval—organizations eliminate ad‑hoc judgments, ensure equitable treatment of all applicants, and maintain a robust, defensible credit policy. This disciplined approach also facilitates continuous improvement: performance metrics such as approval turnaround time, delinquency rates, and customer satisfaction scores are tracked and reported, enabling data‑driven refinements to the approval criteria and workflow rules. Ultimately, a standardized approval process not only protects financial exposure but also enhances operational efficiency and customer trust. now!!!.
Company and Banking Information Fields
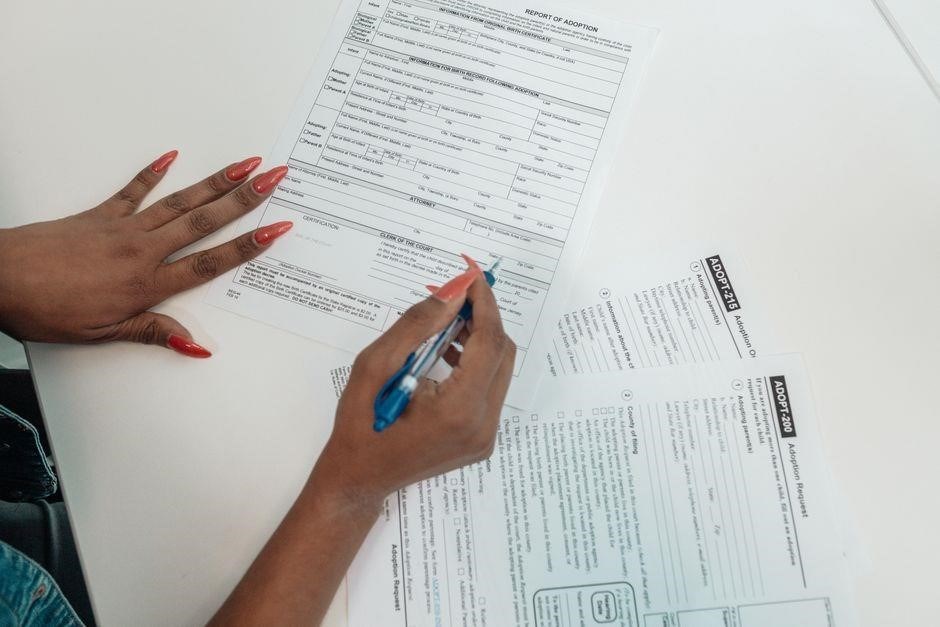
The company and banking information section of a new‑customer credit application PDF is the foundation for verifying identity, establishing legal standing, and setting up payment channels. It begins with the applicant’s trading name, full postal address, postcode, and contact numbers—telephone, mobile, and fax. An email address is required for electronic correspondence and for receiving the signed credit agreement and also. The form captures statutory identifiers: company registration number and VAT registration number, essential for tax compliance and cross‑checking against public registries. A field for the requested credit limit allows the credit team to gauge exposure before any decision is made. The banking block is detailed: bank’s name, branch, account holder name, account number, sort code (or routing number), IBAN, and SWIFT/BIC codes are mandatory. Including the bank’s address and contact details ensures payment instructions are unambiguous and that the bank can verify the account. Some templates also ask for a bank reference letter or a recent statement to confirm account activity. All these fields are designed to be auto‑validated by the PDF engine: postal codes must match the country format, phone numbers must include country codes, and IBANs are checked against the checksum algorithm. The result is a single, self‑contained document that can be digitally signed, stored in the customer relationship management system, and fed into the credit decision engine without manual data entry. This reduces errors, speeds up onboarding, and keeps the credit file audit‑ready.
When the PDF is submitted, the system automatically extracts the banking details and cross‑checks them against the national bank registry. If any mismatch is detected, the application is flagged for manual review. The captured data can also be pushed directly to the company’s ERP via an API, populating the vendor master record and creating a credit line in the accounts receivable module. This seamless data flow eliminates duplicate data entry, reduces the risk of transcription errors, and ensures that the credit limit is reflected in real time across all sales platforms. Additionally, the form includes a checkbox for the customer to authorize the verification of the supplied banking information, thereby satisfying legal protection requirements and providing a clear audit trail for future disputes and ensures compliance.
Digital PDF Integration and Customization
Integrate the PDF form into your workflow via API calls, enabling auto‑population of fields, digital signatures, and real‑time validation. Custom templates let you brand the form, embed QR codes, and set conditional logic, ensuring a seamless, audit‑ready experience. API supports bulk uploads updates real.
Customizable PDF Templates and API Usage
Modern credit application workflows rely on dynamic PDF templates that can be tailored to each business’s branding and regulatory needs. By exposing a RESTful API, developers can programmatically generate, populate, and retrieve forms in real time. The API accepts JSON payloads that map directly to PDF fields, allowing seamless integration with ERP, CRM, or bespoke onboarding portals. Key features include:
- Template versioning: maintain audit trails and rollback to previous layouts.
- Conditional field rendering: hide or display sections based on applicant data.
- Digital signature capture: enforce legal compliance with e‑signature standards.
- Batch processing: submit multiple applications in a single request to reduce latency.
- Webhook notifications: trigger downstream workflows when a form is signed or rejected.
Security is paramount; all endpoints require OAuth 2.0 authentication, and data is transmitted over TLS 1.3. The service also offers an SDK in Java, Python, and Node.js, simplifying integration for common stacks. By leveraging these capabilities, organizations can eliminate manual PDF handling, reduce errors, and ensure every credit application is consistent, traceable, and compliant with audit requirements.
Customization extends beyond branding; users can embed QR codes that link to verification dashboards, pre‑populate fields from existing customer records, and enforce mandatory sections through validation rules. The API also supports inline image uploads, enabling the inclusion of company logos or regulatory stamps directly within the PDF. Additionally, the platform offers a drag‑and‑drop designer that lets non‑technical staff adjust layouts without code, accelerating deployment cycles.
Performance benchmarks show that generating a single PDF via the API takes under 200 milliseconds on average, even when processing complex conditional logic. For high‑volume environments, the service supports horizontal scaling and load balancing, ensuring that peak traffic during product launches or seasonal promotions does not degrade response times. Monitoring dashboards provide real‑time insights into API usage, error rates, and throughput, enabling proactive capacity planning.